Admin guide
Admin guide
This is the operational reference for IT admins running Greenlight. It assumes operational literacy with cloud, identity, and source control. Citizen developers use a different surface — see the For citizen developers guide.
Greenlight runs in a dedicated boundary inside your Azure subscription, Google Cloud project, or AWS account. The services differ by provider, but the architecture and install flow are the same:
| Capability | Azure | GCP | AWS |
|---|---|---|---|
| Kubernetes | AKS | GKE | EKS |
| PostgreSQL | Flexible Server | Cloud SQL | RDS |
| Object storage | Blob Storage | Cloud Storage | S3 |
| Container registry | ACR | Artifact Registry | ECR |
| Secrets | Key Vault | Secret Manager | Secrets Manager |
| DNS | Azure DNS | Cloud DNS | Route 53 |
The reference diagram below uses the Azure service names; the GCP and AWS install pages map the same components to their provider equivalents.
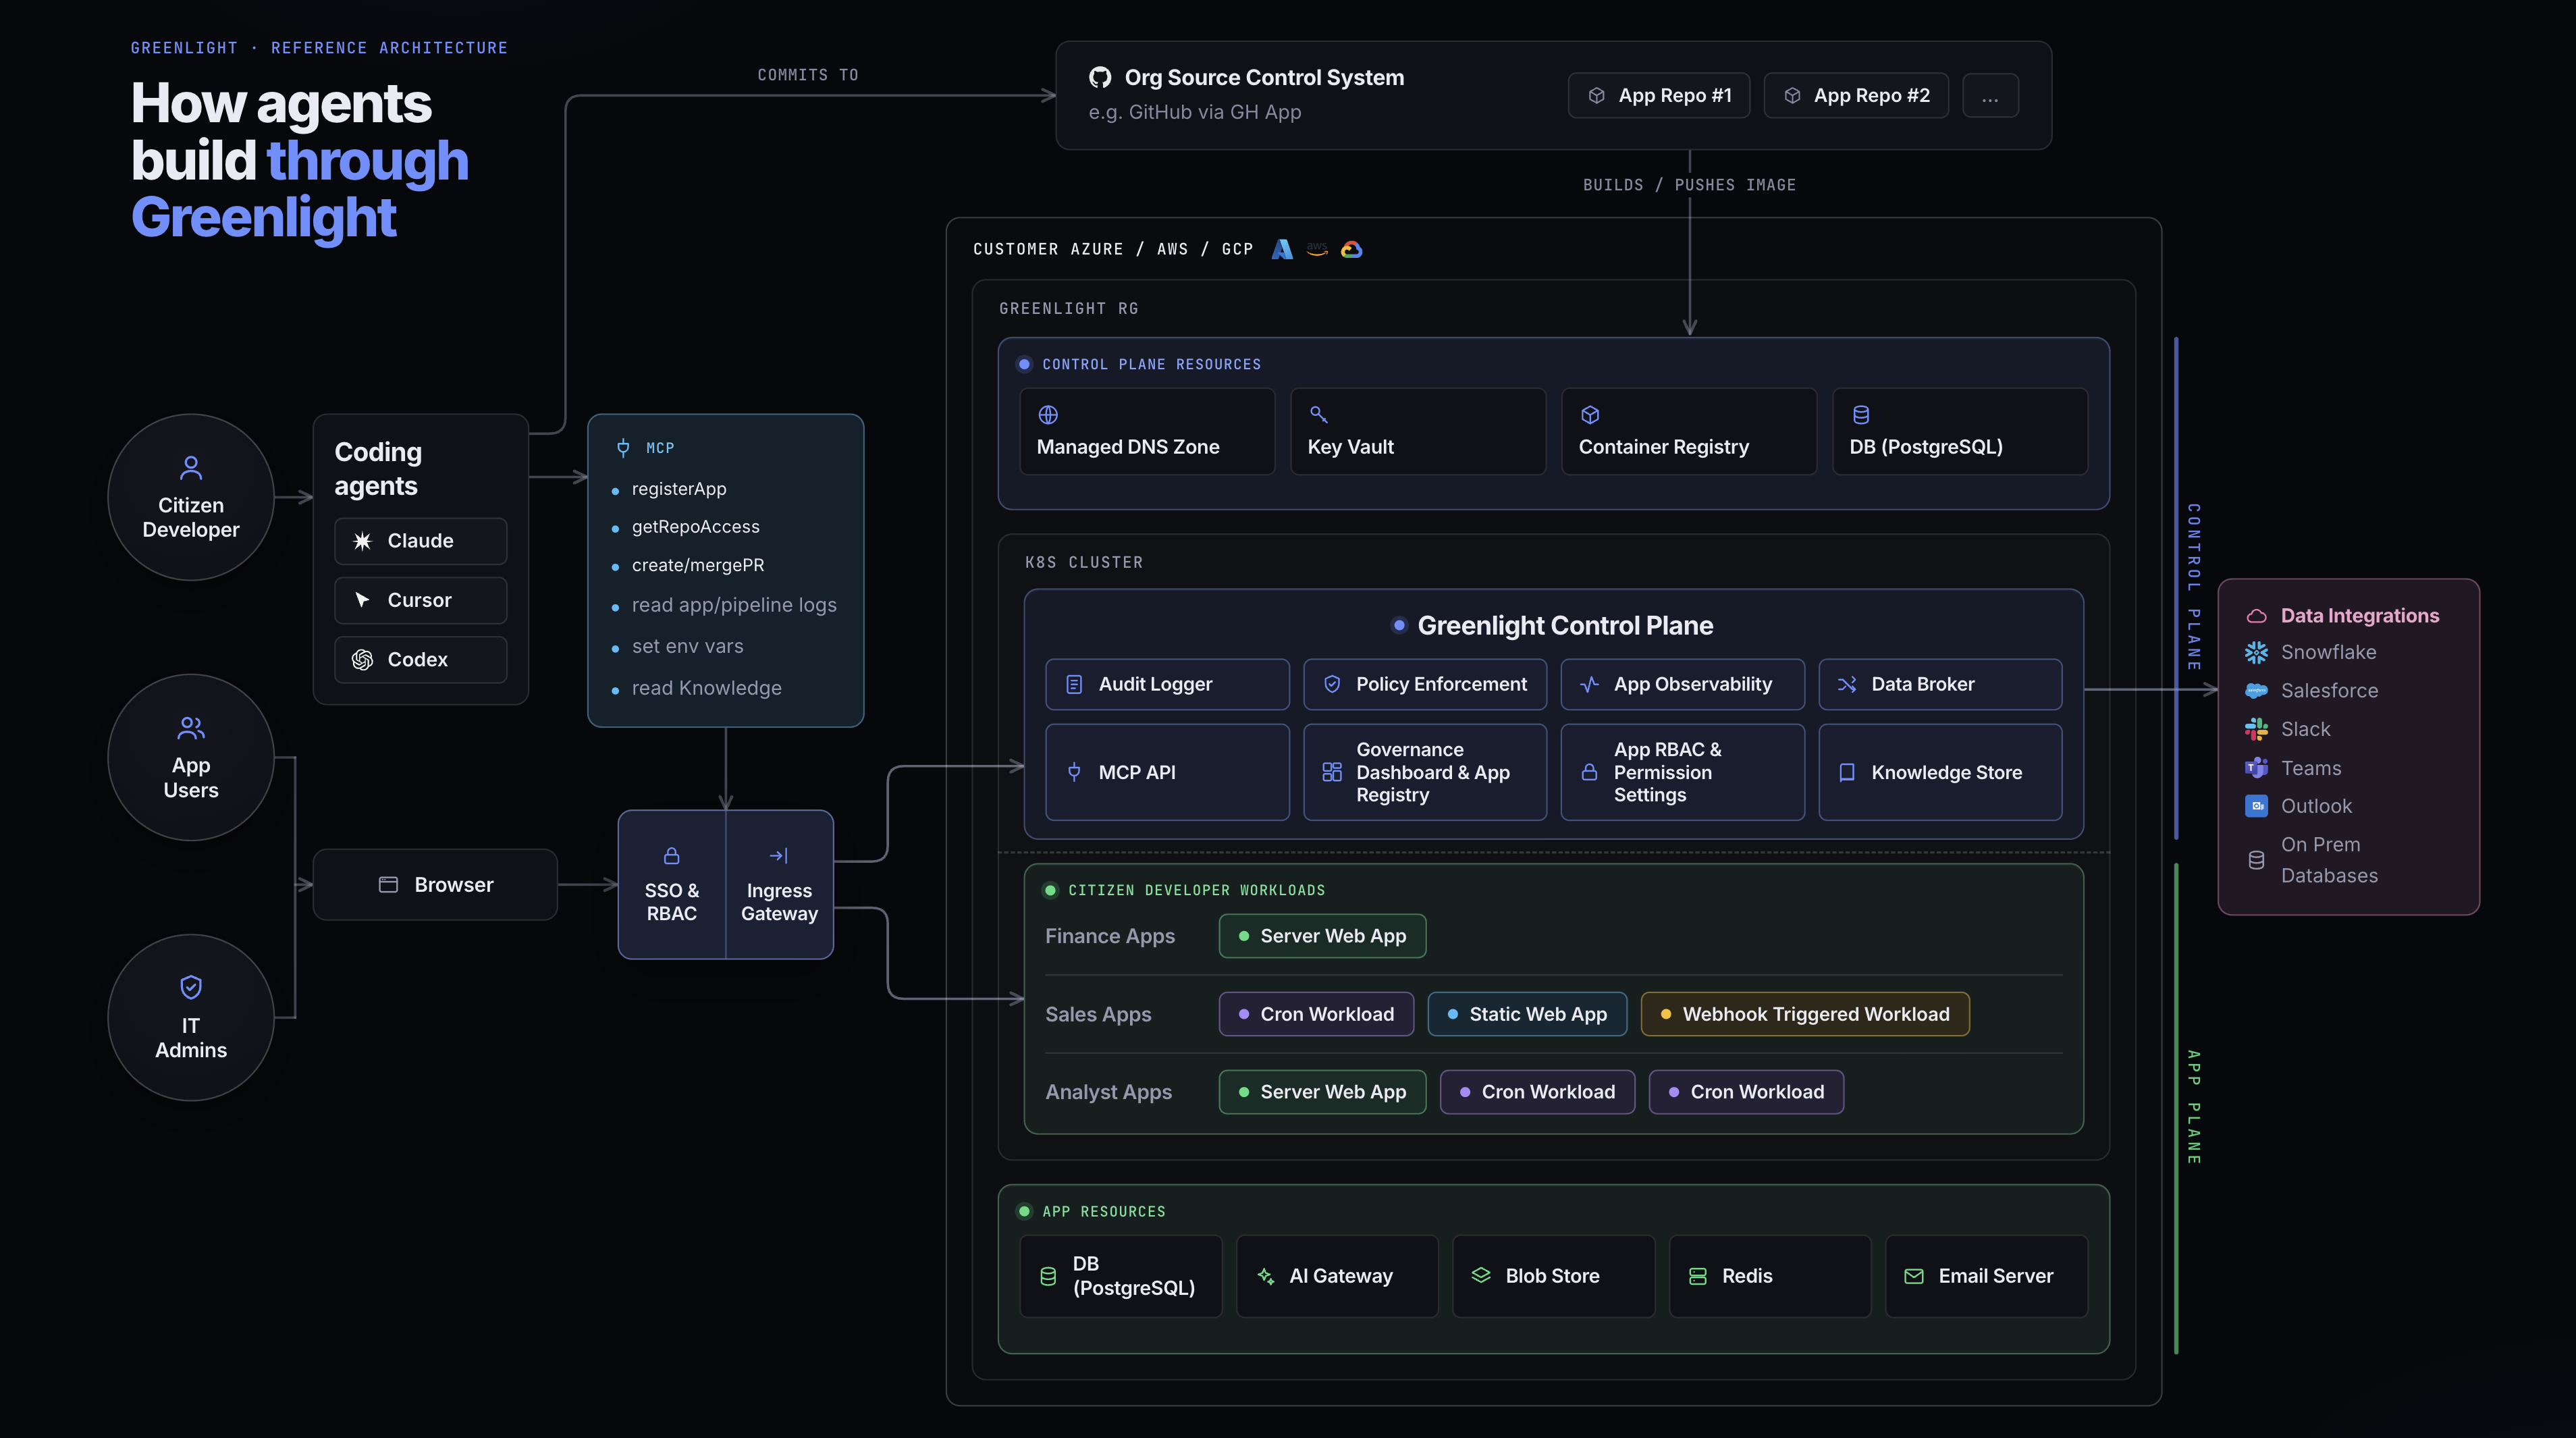
New to the dashboard? Start with the dashboard tour — every major screen in one scroll. The work then splits into three phases: install (one-time), configure (per organization), and operate (ongoing).
Install
Section titled “Install”| Page | Purpose |
|---|---|
| Install on Azure | Azure resources, required roles, Greenlight-managed capacity, and the complete install flow. |
| Install on GCP | Google Cloud resources, required roles, Greenlight-managed capacity, and the complete install flow. |
| Install on AWS | AWS resources, required roles, Greenlight-managed capacity, and the complete install flow. |
| DNS & TLS | The single delegated zone and the certificate story. |
Configure
Section titled “Configure”| Page | Purpose |
|---|---|
| Identity, SSO & RBAC | Connect Entra ID, Okta, or Google with OIDC, and map IdP groups to Greenlight roles. |
| Source control & the policy check | Install the Greenlight GitHub App and understand the check it posts on every PR. |
| Agent plugin rollout | Turn on the Greenlight plugin for Codex, Claude Code, and Cursor. For Claude, apply the dashboard’s organization settings block to pre-approve every Greenlight MCP and CLI action in Auto Mode, including control-plane-hosted CLI installation and refresh. |
| Manage integrations | Register upstream services, attach credentials, grant to apps. |
| Manage policies | Tune the OPA governance bundle — enforcement, enable/disable, and per-rule configuration. |
| Curate Knowledge | Author org Knowledge and review agent proposals. |
Operate
Section titled “Operate”| Page | Purpose |
|---|---|
| Observability & audit | The audit log, runtime logs, metrics, and the evidence story. |
| Kill switch & restore | Stop an app, restore one, and the audit trail behind each. |
| Compliance evidence | The SOC 2 control mapping in the dashboard, and exporting it for your auditor. |
| Upgrades | The customer-owned updater and release eligibility model. |